• 中文版
  • BM
  • News
  • Deals
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Tech
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • Tune Talk
    • U Mobile
    • Unifi
    • Yes
  • Cars
  • Contribute
  • Jobs
Menu
  • 中文版
  • BM
  • News
  • Deals
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Tech
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • Tune Talk
    • U Mobile
    • Unifi
    • Yes
  • Cars
  • Contribute
  • Jobs
Search
  • Tech
    • News
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • U Mobile
    • Unifi
    • Yes
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Buyer’s Guide
  • Opinions
  • Digital Life
  • Video
  • Deals
  • How-To
  • Cars
  • Bahasa Melayu
  • EV
  • Contribute
  • Advertise
Menu
  • Tech
    • News
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • U Mobile
    • Unifi
    • Yes
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Buyer’s Guide
  • Opinions
  • Digital Life
  • Video
  • Deals
  • How-To
  • Cars
  • Bahasa Melayu
  • EV
  • Contribute
  • Advertise
Search
Close
Home Digital Life

Potential personal data exposure on LHDN’s payment portal

  • BY Alexander Wong
  • 13 December 2023
  • 3:13 pm
  • Comment
Share on FacebookShare on Twitter

It appears that one of the Inland Revenue Board’s (LHDN) payment portals has a potential data exposure concern. One of our readers has tipped us about a vulnerability which allows unauthorised individuals to view personal details including full name, IC number, address, email and phone number.
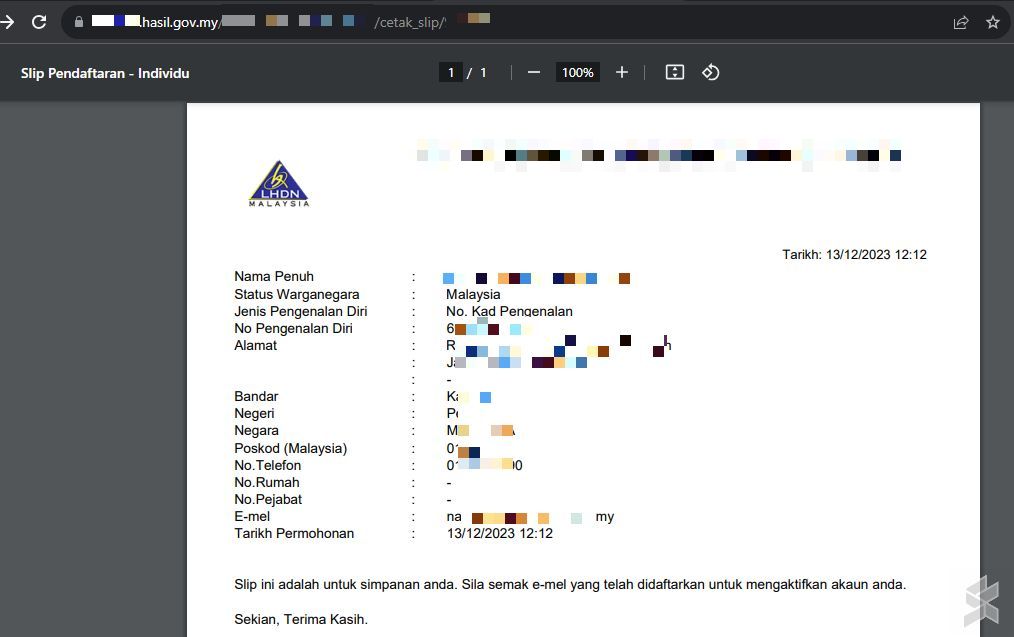
The payment portal in question has a receipt API which generates slips in PDF format. However, the slips are accessible publicly by going through the running numbers and they can be viewed without logging in. As shown above, the PDF slips contain personal information which could be misused for nefarious purposes if they fall into the wrong hands. It could also be a potential source for data harvesting.
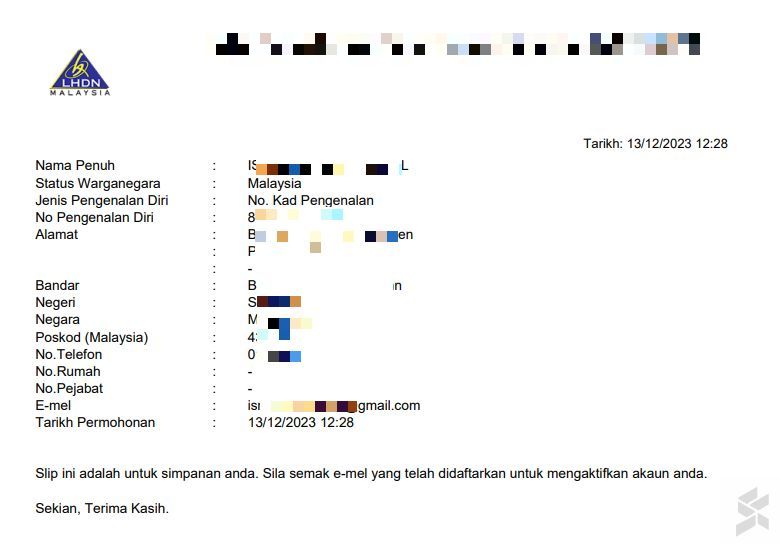
All government agencies and departments must take proactive steps to safeguard personal information. By right, these slips should only be accessible to the intended user. Our tipster suggested that a possible solution is to use UUID (Universal Unique Identifier) as the slip ID so that it is more random and harder to tamper with compared to the current running number implementation.

We’ve notified and contacted LHDN’s Communications and Security Division on the matter.

Tags: Cybersecuritydata breachData exposureData Protectioninland revenue boardIRBLHDNsecurity
Alexander Wong

Alexander Wong

POPULAR

Bringing the vivo X500 Pro Max to Zepp KL: A closer look at vivo’s concert fancam features

October 30, 2026

Potential personal data exposure on LHDN’s payment portal

December 13, 2023

Google Elmina data centre is now live: Puncak Alam, Serendah, Port Dickson in the works

November 4, 2026

Tuju finally “fixes” its navigation problem on Android, and it’s brilliant

November 2, 2026

Google funds RM651 million shared water facilities in Negeri Sembilan to support new data centre

November 2, 2026

ColorOS 17 coming to Malaysia with Living Flow UI, System-Level AI Agents and 6-year smoothness guarantee

October 15, 2026

Copyright © 2026 · SoyaCincau.com
Mind Blow Sdn Bhd (1076827-P)

  • ADVERTISE
  • DISCLAIMER

Copyright © 2026 · SoyaCincau.com – Mind Blow Sdn Bhd (1076827-P)

  • ADVERTISE
  • DISCLAIMER