• 中文版
  • BM
  • News
  • Deals
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Tech
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • Tune Talk
    • U Mobile
    • Unifi
    • Yes
  • Cars
  • Contribute
  • Jobs
Menu
  • 中文版
  • BM
  • News
  • Deals
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Tech
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • Tune Talk
    • U Mobile
    • Unifi
    • Yes
  • Cars
  • Contribute
  • Jobs
Search
  • Tech
    • News
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • U Mobile
    • Unifi
    • Yes
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Buyer’s Guide
  • Opinions
  • Digital Life
  • Video
  • Deals
  • How-To
  • Cars
  • Bahasa Melayu
  • EV
  • Contribute
  • Advertise
Menu
  • Tech
    • News
    • Mobile
    • Computers
    • Cameras
    • Wearables
    • Audio
    • Drones
  • Telco
    • Celcom
    • Digi
    • Maxis
    • Time
    • U Mobile
    • Unifi
    • Yes
  • Reviews
    • First Impressions
    • Hands-on
    • Comparisons
  • Buyer’s Guide
  • Opinions
  • Digital Life
  • Video
  • Deals
  • How-To
  • Cars
  • Bahasa Melayu
  • EV
  • Contribute
  • Advertise
Search
Close
Home News

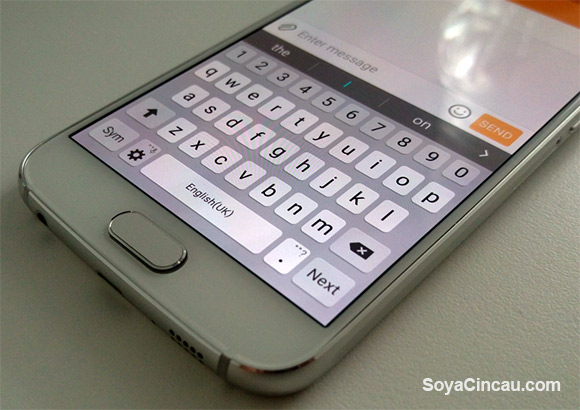
Samsung’s default keyboard is vulnerable to open attacks

  • BY Sirap Bandung
  • 17 June 2015
  • 11:45 am
  • Comment
Share on FacebookShare on Twitter

150617-galaxy-keyboard

UPDATE: Samsung addresses the keyboard vulnerability issue using KNOX.

If you happen to own a Samsung Galaxy S4, Galaxy S4 Mini, Note 3, Galaxy S5 or the more recent Galaxy Note 4 and Galaxy S6, we have a bit of bad news for you. Samsung’s built-in stock keyboard apparently has an exploit that might potentially allow people to execute code remotely on your phone no thanks to a flaw in the SwiftKey software.

samsung-galaxy-exploit

Basically if you are connected to an unsecured access point like an open WiFi network it’s possible for someone to intercept and alter SwiftKey language packs as they update and upload a malicious payload by impersonating the server which updates the software.

If the flaw is exploited, people could get access to sensors and resources on your phone like the GPS, camera and microphone, eavesdrop on voice calls and messages, attempt to steal your personal data and otherwise mess with the apps on your device. However, the problem lies strictly with phones that come with Samsung’s version of SwiftKey as the problem doesn’t affect those who downloaded it from Google Play or the App store.

Samsung has already been notified by the issue and they are working on a patch for it but for now its best to avoid public hotspots that aren’t secure, use a VPN or just keep to your personal secure networks till there’s official word of the fix.

[VIA, 1][SOURCE]

Tags: Keyboardmobile deviceSamsungsamsung exploitSamsung Galaxy S4Samsung Galaxy S5Samsung Galaxy S6samsung swiftkeySwiftKey
Sirap Bandung

Sirap Bandung

[email protected]

POPULAR

Bringing the vivo X500 Pro Max to Zepp KL: A closer look at vivo’s concert fancam features

October 30, 2026

Samsung’s default keyboard is vulnerable to open attacks

June 17, 2015

Google Elmina data centre is now live: Puncak Alam, Serendah, Port Dickson in the works

November 4, 2026

Tuju finally “fixes” its navigation problem on Android, and it’s brilliant

November 2, 2026

Google funds RM651 million shared water facilities in Negeri Sembilan to support new data centre

November 2, 2026

ColorOS 17 coming to Malaysia with Living Flow UI, System-Level AI Agents and 6-year smoothness guarantee

October 15, 2026

Copyright © 2026 · SoyaCincau.com
Mind Blow Sdn Bhd (1076827-P)

  • ADVERTISE
  • DISCLAIMER

Copyright © 2026 · SoyaCincau.com – Mind Blow Sdn Bhd (1076827-P)

  • ADVERTISE
  • DISCLAIMER